Vulnerability scanning
AppSecOne
A cloud service that checks web applications for vulnerabilities. No test code is needed: input areas are extracted automatically and scanned. It covers the OWASP Top 10 and can also be used on migrated code.
Features
01
No test code
You don’t need to write any test code to run a scan.
02
Input areas found automatically
Input areas on each screen are extracted and attack patterns are tried.
03
OWASP Top 10
Scans target the attack techniques in the OWASP Top 10.
Typical use
- Scanning migrated code
- Regular self-checks before release
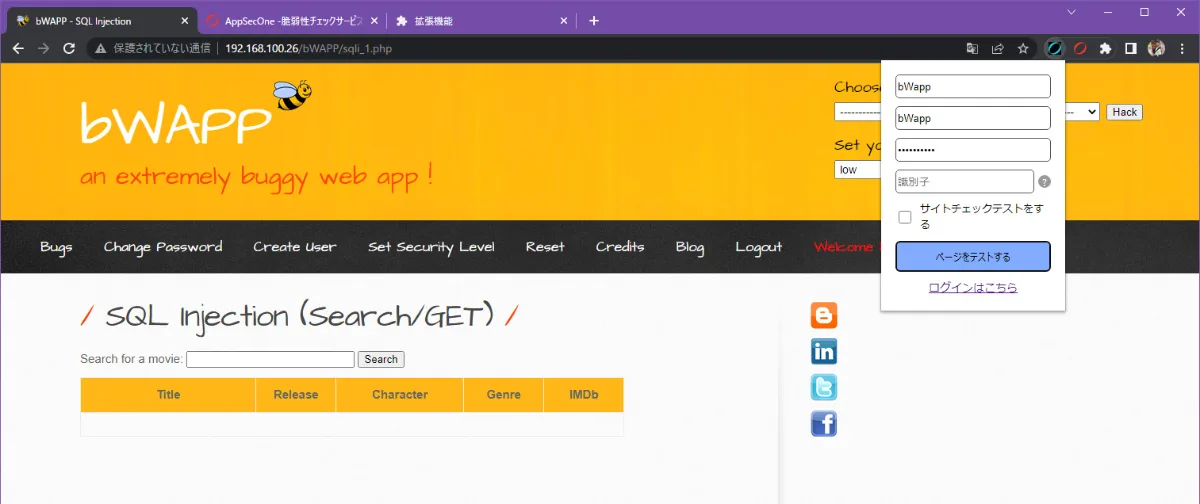
Screens
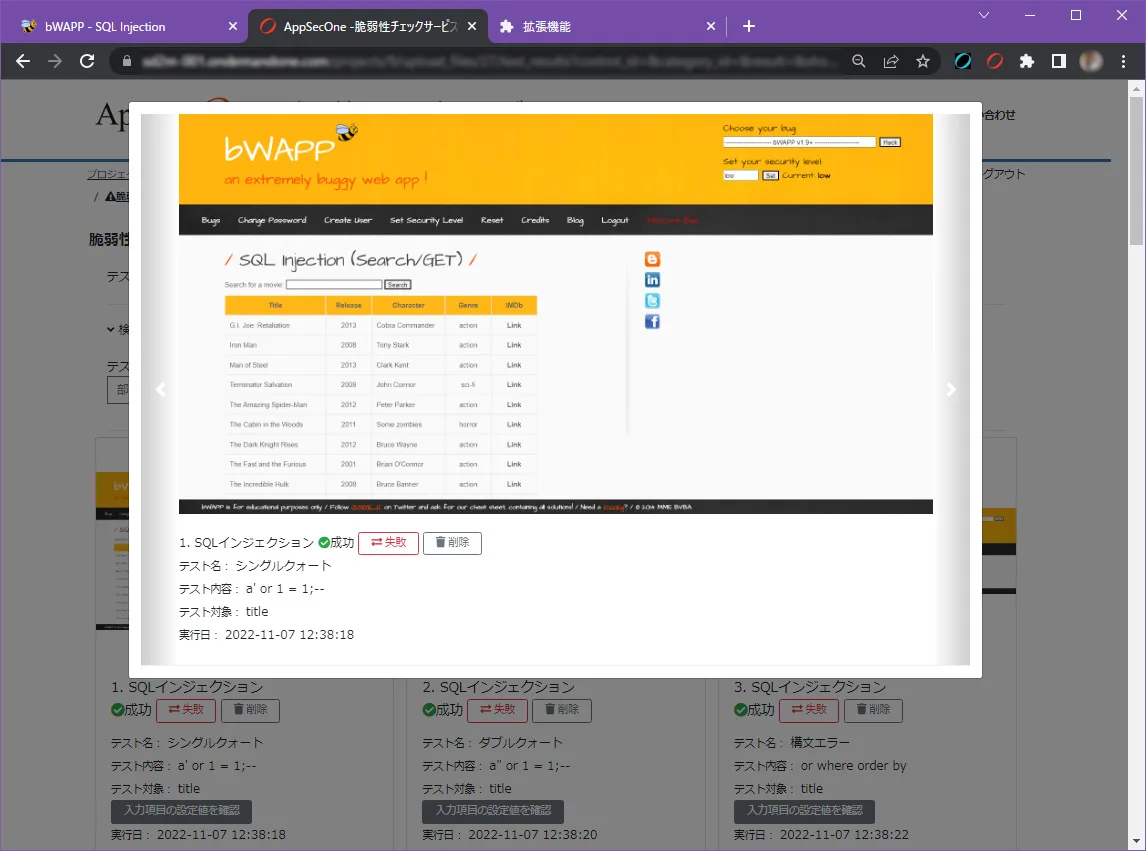
Screenshots
Contact
Start with whether migration is feasible
Tell us the platform version and the number of screens, and we will send an initial answer. We are happy to sign an NDA first.
TEL +81-3-5962-3776